
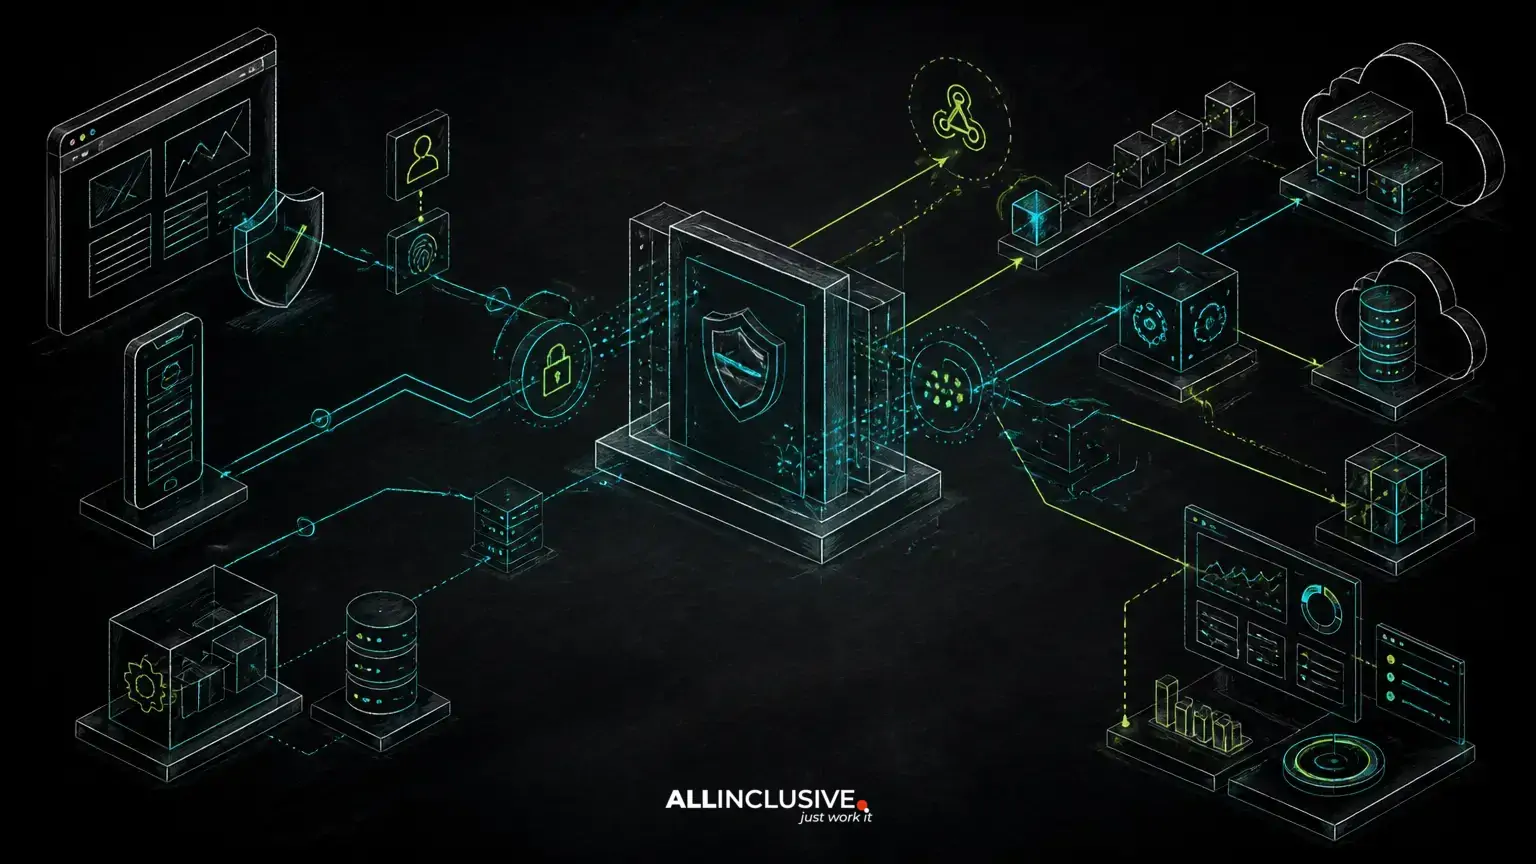
An API security checklist should cover more than authentication. A secure custom web application must validate every request, enforce authorization at the resource level, protect secrets, control traffic, handle webhooks safely, and produce enough telemetry to investigate failures or abuse.
Security also depends on integration reliability. Retries can duplicate a payment or update, an unverified webhook can alter records, and an expired credential can interrupt a critical workflow. The most useful checklist therefore combines application security with contracts, idempotency, queues, reconciliation, versioning and operational visibility.
This guide focuses on the controls and design decisions product teams should review before exposing an API or connecting a web application to third-party services.
Start with an API inventory and trust-boundary map
Before selecting middleware or authentication libraries, document what exists. List public endpoints, internal endpoints, administrative operations, webhooks, scheduled jobs and outbound integrations. For each interface, identify:
- Who calls it and whether the caller is a user, service, partner or third-party platform.
- What data it accepts, returns or modifies.
- Which systems own the data and which systems only cache or mirror it.
- What happens if the request is delayed, duplicated, rejected or processed out of order.
- Which credentials, tokens, signing keys and personal or financial data are involved.
Mark each trust boundary explicitly. A browser, mobile client, partner system and internal worker should not automatically receive the same privileges. This inventory helps prevent a common failure mode: securing the network connection while leaving authorization, data ownership or workflow transitions under-specified.
API security checklist: identity, authentication and authorization
Use the right authentication method for each caller
- Use short-lived user sessions or access tokens for interactive applications where appropriate.
- Use narrowly scoped credentials for service-to-service calls.
- Use OAuth 2.0 flows carefully when a user grants a third-party application delegated access; validate redirect handling, scopes, token storage and token expiration.
- Use signed requests or webhook signatures for inbound event notifications when the provider supports them.
- Never place long-lived secrets in browser code, mobile bundles, source control or client-visible configuration.
Authentication proves who or what is calling. It does not prove that the caller may access a particular account, order, document or administrative action.
Authorize every resource and operation
Enforce authorization on the server for every request. Check both the requested action and the relationship between the authenticated principal and the resource. A user who can view one organization’s invoice should not gain access by changing an identifier in the URL. Likewise, a service account that can create orders may not need permission to refund them.
Prefer explicit policies and scopes over scattered conditional checks. Test horizontal access, vertical privilege escalation, tenant isolation and access after role changes. Authorization rules should be reviewed whenever a new endpoint, object type or workflow state is introduced.
For teams evaluating OAuth 2.0 API authentication, the key decision is not simply whether OAuth is present. It is whether token audiences, scopes, lifetimes and delegated permissions match the application’s actual trust model.
Validate requests, responses and state transitions
Define a contract for each endpoint. Validate types, lengths, formats, enumerated values, nested objects and allowed relationships. Reject unexpected fields where mass assignment could change protected attributes. Normalize inputs consistently, but do not silently transform values in ways that hide client defects or alter security-relevant meaning.
Validation should also cover business state. An API may receive a syntactically valid request to cancel an already settled transaction or approve a record belonging to another tenant. Treat workflow rules as part of the security boundary, not merely as user-interface behavior.
Response design matters too. Return only the fields the caller needs, avoid exposing internal identifiers or stack traces, and use predictable error structures. Detailed diagnostics belong in protected logs, not in production responses.
Protect credentials, sensitive data and administrative surfaces
- Store secrets in a managed secret store or protected environment configuration rather than source code.
- Rotate credentials and signing keys using a documented process that supports overlap when necessary.
- Encrypt traffic in transit and protect sensitive data at rest according to its risk and regulatory context.
- Redact tokens, passwords, payment details and personal data from logs, traces and error reports.
- Separate production credentials from development and test credentials.
- Restrict administrative endpoints with stronger authentication, narrower network access or additional approval controls where justified.
Do not treat encryption as a substitute for access control. Encrypted data can still be exposed by an overly broad API response, an overprivileged worker or a compromised application credential.
Secure webhooks and outbound integrations
Inbound webhooks deserve the same scrutiny as public API requests. Verify the provider’s signature against the raw request body, validate the event type and intended recipient, and reject stale requests when the provider includes a timestamp or nonce mechanism. Store event identifiers so a repeated delivery can be recognized.
A reliable webhook handler should acknowledge quickly after authenticating and validating the event, then queue heavier processing. This reduces provider timeouts and separates receipt from business processing. The worker should still verify that the event is applicable, because valid events can arrive late, out of order or after an object has changed.
For outbound calls, define connection and response timeouts, limit payloads, protect credentials and classify failures. A timeout does not prove that the provider did not process the request. That is why idempotency keys, provider request identifiers and reconciliation jobs are essential for operations such as payments, provisioning and record synchronization.
The architecture patterns in third-party API integration strategy are particularly useful when an API is only one part of a longer workflow involving retries, queues and external state.
Make retries safe with idempotency, queues and reconciliation
Retries improve resilience but can amplify damage when operations are not idempotent. Decide which requests may be retried and define an idempotency key for operations where duplicate execution has a business cost. Store the key with the resulting status or resource reference, and define how long it remains valid.
Use bounded retries with backoff and jitter for transient failures. Do not retry validation errors, authorization failures or permanent business rejections. Respect provider rate limits and retry guidance when available. A queue can isolate users from temporary provider failures, but it does not remove the need for visibility or eventual consistency rules.
Reconciliation closes the gap between local assumptions and external reality. Scheduled or operator-triggered checks can compare orders, payments, subscriptions or customer records and identify missing, duplicated or mismatched states. Reconciliation is especially important when a provider’s response was lost after the remote operation succeeded.
Control traffic and abuse without harming legitimate workflows
Apply rate limits according to identity, tenant, endpoint and operation risk. A public login route, password-reset route, search endpoint and administrative export should not necessarily share one limit. Consider request size limits, pagination requirements, concurrency controls and upload restrictions as part of the same abuse-prevention layer.
Return consistent responses for throttling and avoid revealing unnecessary information about account existence. Rate limiting should be observable and adjustable. If limits are too strict, legitimate batch jobs fail; if they are too permissive, an exposed credential or expensive query can create operational and financial impact.
Version contracts and design explicit error states
Version an API when changing behavior could break a consumer. Define compatibility rules for fields, enum values, pagination, authentication scopes and error formats. Additive changes are not always safe: a new required field, changed default, stricter validation rule or newly exposed event can affect existing clients.
Document errors by category, including authentication failure, authorization failure, validation failure, conflict, rate limiting, dependency failure and unknown processing state. Clients need to know whether to fix the request, refresh credentials, wait and retry, poll for status or contact an operator.
For asynchronous operations, return a durable operation or resource reference rather than making the client infer success from a timeout. This makes user workflows clearer and reduces unsafe duplicate submissions.
Build observability into the security model
Log security-relevant events such as failed authentication, denied authorization, token use anomalies, signature failures, rate-limit violations and administrative changes. Include a correlation identifier, endpoint, tenant or account context where safe, outcome and latency. Do not log secrets or unrestricted payloads merely for convenience.
Monitor both security and integration signals:
- Spikes in rejected requests or access denials.
- Repeated webhook signature failures.
- Unusual token, tenant or geographic activity where such analysis is appropriate.
- Growing queue age, retry counts and dead-letter volume.
- Unreconciled records and provider response changes.
- Latency and error rates by endpoint and dependency.
Alerts should lead to a documented response: who investigates, how credentials are revoked, how affected records are identified, and how a failed integration is replayed or reconciled.
Choose Laravel or Python according to responsibility
Laravel can be a strong fit when the API belongs to a conventional business application with authentication, authorization policies, validation, relational data and administrative workflows. Its value comes from applying consistent application structure and established security practices, not from assuming that a framework automatically makes endpoint design safe.
Python can fit integration-heavy services, data workflows, asynchronous processing and systems that need specialized libraries or separate worker processes. The same controls still apply: explicit contracts, dependency isolation, secret management, authorization, safe retries and operational telemetry.
In either stack, keep security responsibilities visible in code review and automated tests. Test authorization matrices, malformed input, replayed webhooks, duplicate submissions, expired credentials, dependency timeouts and partial failures. Select the framework based on the system’s ownership, team expertise, integration shape and long-term maintenance needs.
Use this release-readiness review
- Every endpoint and webhook has an identified caller, owner, data classification and trust boundary.
- Authentication, authorization and tenant isolation are tested independently.
- Requests and responses follow documented contracts with safe validation and error handling.
- Secrets are protected, rotated and excluded from logs and client-side code.
- Webhook signatures, replay handling and event deduplication are implemented.
- Retries are bounded, idempotency is defined and unknown outcomes can be reconciled.
- Rate limits, request limits and expensive-operation controls are configured.
- API versions and compatibility expectations are documented.
- Logs, metrics, traces and alerts support investigation without exposing sensitive data.
- Operational owners know how to revoke access, replay work and recover from dependency failure.
Security is strongest when it is designed alongside the workflow the API supports. For teams building or extending a custom application, API development should include contract design, access control, integration failure handling and observability from the beginning. The broader software development context also matters: API boundaries affect the application’s data model, user experience, deployment process and maintenance burden.
After launch, security and reliability require continued review as providers change, credentials rotate, new consumers appear and business workflows expand. A structured support and maintenance process can help teams keep controls, dependencies and operational runbooks aligned with the system they actually run.
See support and maintenance for custom software when ongoing monitoring, updates and incident readiness need to be treated as part of the product lifecycle.


